Hello, I'm

Muhammad Umar

Aspiring SOC Analyst | Cybersecurity Trainee

Cybersecurity-focused aspiring SOC Analyst with hands-on experience in network traffic analysis, SIEM monitoring, Windows security log analysis, phishing analysis, and incident response. I work with tools and technologies including Wireshark, Splunk, Wazuh, Windows Event Viewer, Linux, TCP/IP, HTTP, DNS, and MITRE ATT&CK. Through practical labs and security-focused projects, I am building strong blue-team and security operations skills. I am currently developing my capabilities toward a career in SOC operations and cybersecurity. Open to SOC Analyst Intern and Cybersecurity Intern opportunities.
Muhammad Umar — Professional Profile Photo
MU

About Me

Muhammad Umar is an aspiring cybersecurity professional focused on SOC operations, security monitoring, blue-team practices, network security, and incident response. He currently works as a Cybersecurity Trainee at Astra Quantum Tech, participating in practical cybersecurity sessions, labs, security assessments, and industry mentorship. His hands-on work includes network traffic analysis with Wireshark, SIEM monitoring with Splunk and Wazuh, Windows security event analysis, phishing investigation, and incident response case studies. He has practical familiarity with TCP/IP, HTTP, DNS, TLS, SMTP, Linux, Windows, MITRE ATT&CK, and security-focused tools. He is continuously strengthening his cybersecurity skills through practical projects, labs, and professional training while pursuing opportunities in SOC and cybersecurity roles.

Mission

To develop strong practical cybersecurity and blue-team skills while helping organizations detect, analyze, and respond to security threats effectively.

Vision

To become a highly capable cybersecurity professional specializing in SOC operations, threat detection, incident response, and defensive security.

Work Experience

Sep 2026 – Present

Arch Technologies

Internship / Remote

Intern

Peshawar, Khyber Pakhtunkhwa, Pakistan

Remote cybersecurity internship focused on practical, hands-on security tools and techniques — building and analyzing security tools in Python, with a project-based approach each month.

Aug 2026 – Present

Astra Quantum Tech

Trainee / Remote Learning Program

Cybersecurity Trainee

Peshawar, Khyber Pakhtunkhwa, Pakistan

  • Participating in the Summer of Cybersecurity 2026 program through live cybersecurity sessions, practical labs, security assessments, and industry mentorship.
  • Developing foundational knowledge of cybersecurity, networking, system security, threat analysis, and security best practices through hands-on training.
  • Collaborating with peers in a remote learning environment while applying cybersecurity concepts to practical exercises and security scenarios.

Education

SZIC University Of Peshawar

Bachelor of Science in Computer Science (BSCS)

Information Technology

Peshawar, Khyber Pakhtunkhwa, Pakistan

Enrolled / Ongoing
Key Focus
  • Computer Information Systems
  • Software Development
  • Network & Cybersecurity Fundamentals

Fazaia Inter College, Shaheen Camp

Intermediate in Computer Science (ICS)

Peshawar, Pakistan

June 2024 – June 2026 · Full-time
Key Highlights
  • Computer Science, Physics, and Mathematics foundation.
  • Developed an academic foundation in computing and technical subjects.
  • Completed Intermediate-level education in the ICS stream.

Fazaia Inter College, Shaheen Camp

Matriculation in Science

Peshawar, Pakistan

May 2022 – May 2024 · Full-time
Key Highlights
  • Completed secondary education in the Science group.
  • Built foundational knowledge across science and technical subjects.
  • Developed the academic foundation for further study in computer science and cybersecurity.

Projects

01 Cybersecurity / Network Analysis

Network Traffic Analyzer

Analyzed network traffic using Wireshark to capture and inspect packets in a controlled environment. Examined communication patterns and packet-level details while investigating a simulated malware infection.

Key Outcomes

Identified a compromised host during a simulated malware investigation.
Investigated NBNS, Kerberos, and SAMR protocol activity.
Strengthened packet analysis and network troubleshooting skills.
Wireshark TCP/IP HTTP DNS TLS Packet Analysis
View on GitHub
02 Networking / Infrastructure

Cisco Packet Tracer Network Simulation

Designed and configured network topologies in Cisco Packet Tracer to simulate real-world enterprise environments and routing infrastructure.

Key Outcomes

Implemented VLAN segmentation, inter-VLAN routing, and subnetting strategies.
Configured dynamic routing protocols and core network services like DHCP and DNS.
Applied basic network security controls and access lists to secure traffic.
Cisco Packet Tracer Routing & Switching VLANs Subnetting Network Protocols
03 Blue Team / SIEM Lab

Home SIEM Lab

Built a home SIEM lab using Splunk and Wazuh to centralize Windows event logs and monitor endpoint activity in a virtualized environment.

Key Outcomes

Centralized Windows security event logs.
Created security monitoring dashboards.
Investigated security alerts to develop practical SIEM detection and analysis experience.
Splunk Wazuh SIEM Windows Event Logs VirtualBox
04 Systems Admin / Identity

Active Directory Enterprise Lab

Built a virtualized Active Directory environment on Windows Server to practice centralized identity, access management, and enterprise domain administration.

Key Outcomes

Managed user accounts, Organizational Units (OUs), and group membership permissions.
Configured and deployed Group Policy Objects (GPOs) for system security and compliance.
Set up core domain infrastructure including Active Directory Domain Services (AD DS) and DNS.
Windows Server Active Directory GPO DNS User Management
05 Blue Team / Detection

Windows Security Event Log Analysis

Simulated attacker behaviors on a Windows virtual machine and analyzed resulting security events using Windows Event Viewer.

Key Outcomes

Investigated Windows security events.
Mapped observed findings to MITRE ATT&CK techniques.
Developed practical understanding of indicators of compromise and attacker behavior.
Windows Event Logs Event Viewer MITRE ATT&CK
06 Email Security / Phishing

Phishing Email Analyzer

Analyzed suspicious emails by examining email headers, sender authentication records, URLs, and attachments to identify phishing indicators.

Key Outcomes

Investigated suspicious email headers.
Evaluated sender authentication mechanisms.
Applied SPF, DKIM, and DMARC concepts to assess email authenticity.
Email Headers SMTP SPF DKIM DMARC
07 Incident Response / Blue Team

Incident Response Case Study

Investigated a simulated security incident using the NIST incident response framework and documented the attack timeline and indicators of compromise.

Key Outcomes

Investigated a simulated security incident.
Documented the attack timeline and indicators of compromise.
Practiced identification, analysis, containment, and recovery stages.
NIST Incident Response Log Analysis IOC Analysis

Skills

Visual representations of current skill confidence based on practical experience and projects.

Cybersecurity & SOC

SOC Operations0%
Security Monitoring0%
Incident Response0%
Log Analysis0%
Threat Analysis0%
IOC Analysis0%

Networking & Protocols

TCP/IP0%
HTTP0%
DNS0%
TLS0%
SMTP0%

Security Tools

Wireshark0%
Splunk0%
Wazuh0%
Windows Event Viewer0%
MITRE ATT&CK0%

Operating Systems

Windows 10/110%
Linux0%

Programming & Technical Tools

Python0%
Git0%
GitHub0%
VirtualBox0%

Other

Technical Documentation0%
Troubleshooting0%
Microsoft Office0%
Canva0%
Graphic Design0%

Certifications

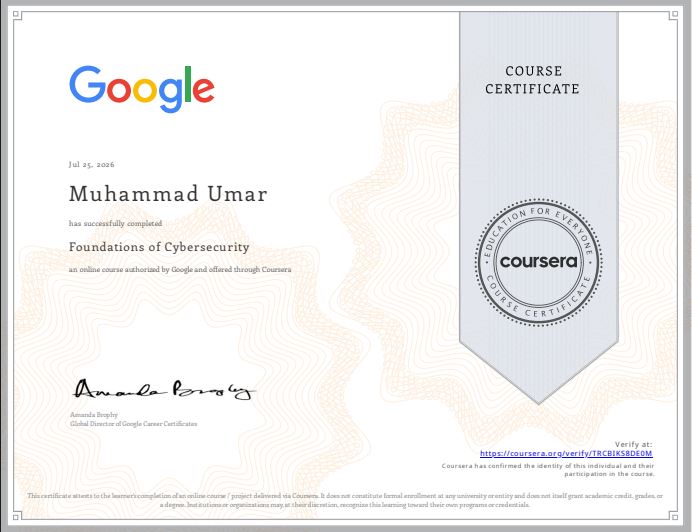
Google Cybersecurity Professional Certificate

Google Cybersecurity Professional Certificate

Google via Coursera

Completed
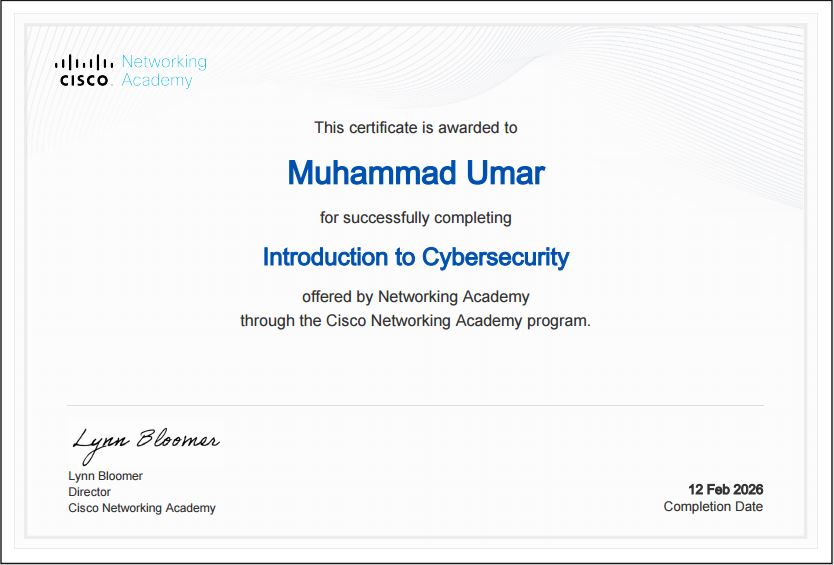
Cisco Introduction to Cybersecurity Certificate

Introduction to Cybersecurity

Cisco Networking Academy

Completed
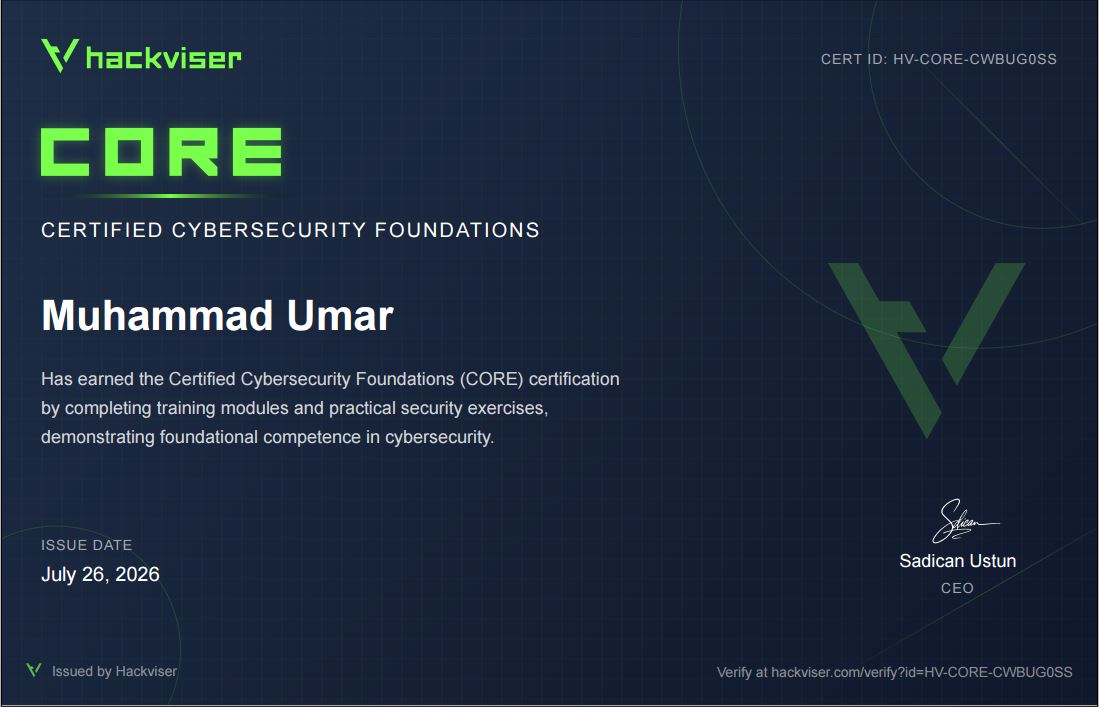
Hackviser Certified Cybersecurity Foundations Certificate

Certified Cybersecurity Foundations

Hackviser

Completed
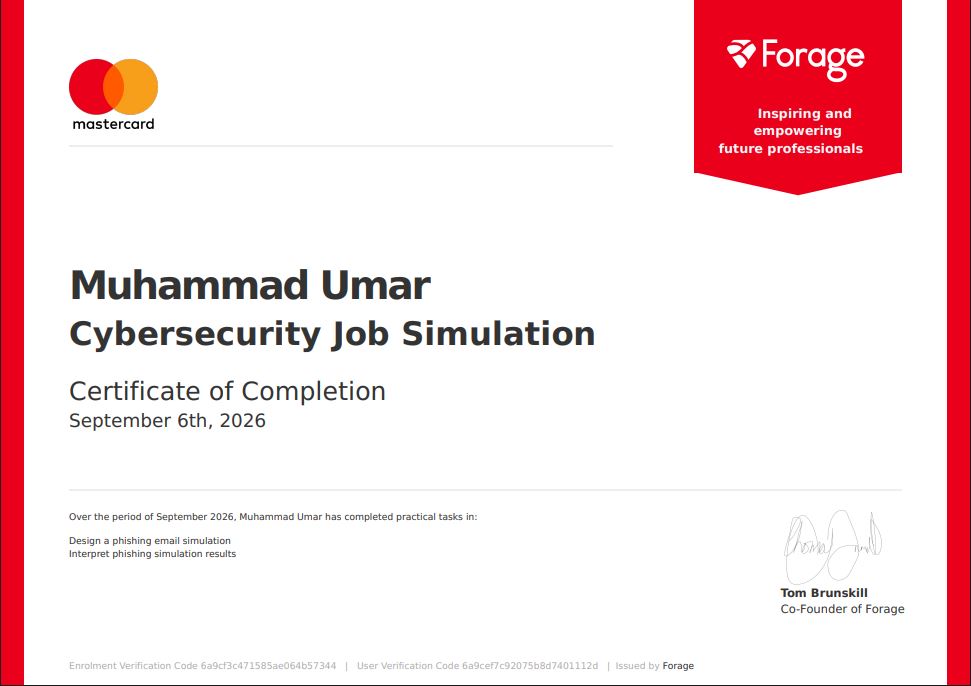
Mastercard Cybersecurity Job Simulation Certificate via Forage

Cybersecurity Job Simulation

Mastercard via Forage

Completed · September 2026

Achievements & Recognition

Building practical cybersecurity skills through hands-on labs, projects, training, and professional development.

0+ Years Experience
0 Certifications
0 Projects
0 Awards
Professional

Cybersecurity Internship

Arch Technologies

2026

Participating in a remote cybersecurity internship focused on building and analyzing practical security tools in Python, applying hands-on technical concepts, and collaborating on monthly project-based tasks.

Professional

Summer of Cybersecurity 2026

Astra Quantum Tech

2026

Participating in a cybersecurity training program involving live cybersecurity sessions, practical labs, security assessments, and industry mentorship.

Professional

Cybersecurity Certification Progress

Google, Cisco Networking Academy & Hackviser

2026

Building cybersecurity knowledge through professional training and certifications covering cybersecurity foundations and practical security concepts.

Let's Connect

Send Me a Message