Hello, I'm
Muhammad Umar
Aspiring SOC Analyst & Defensive Cybersecurity Specialist
Cybersecurity professional with rigorous practical experience in network traffic analysis, SIEM log monitoring, Windows event triage, phishing analysis, and incident response. Actively investigating threats using Splunk, Wazuh, Wireshark, and MITRE ATT&CK frameworks.
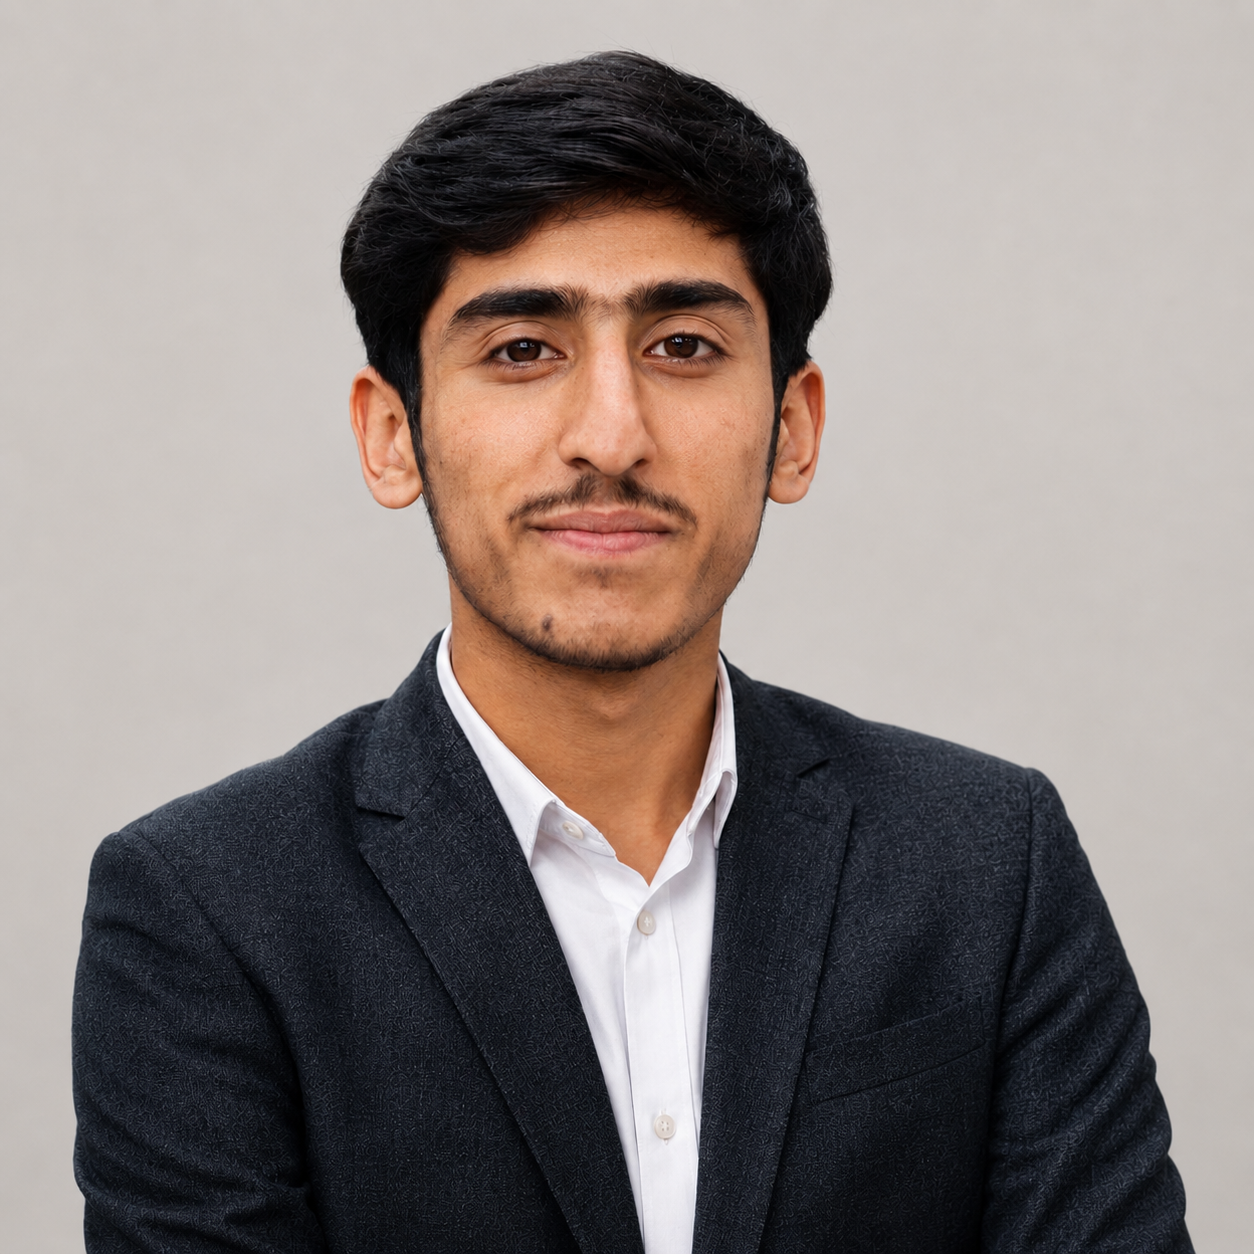
About Me
Dedicated to mastering defensive cybersecurity, threat hunting, and modern security operations.
I am an aspiring cybersecurity professional focused on SOC operations, security monitoring, blue-team practices, network defense, and incident response, advancing practical skills through hands-on labs, professional training, and industry internships.
My hands-on lab work encompasses deep-packet dissection in Wireshark, SIEM engineering in Splunk and Wazuh, enterprise Active Directory security, and NIST-aligned incident triage. I am driven by uncovering anomalous indicators and fortifying critical systems.
Mission
To hone elite defensive and blue-team capabilities, proactively discovering vulnerabilities, mitigating threats, and safeguarding enterprise assets against emerging threat actors.
Vision
To evolve into a high-impact Security Operations Center (SOC) specialist and Security Engineer, leading detection engineering, malware triage, and cyber resilience.
Work Experience
Real-world training, tool development, and defensive security workflows.
Arch Technologies
- Participating in a remote cybersecurity internship focusing on hands-on defensive security tools, log parsers, and automation in Python.
- Conducting monthly project-based tasks to analyze security tools, evaluate detection metrics, and simulate defense strategies.
- Collaborating with security mentors to dissect vulnerability vectors and explore practical blue-team countermeasures.
Astra Quantum Tech
- Completed intensive modules in the Summer of Cybersecurity 2026 program featuring live sessions, hands-on labs, and threat scenario simulations.
- Strengthened core foundations across networking, system hardening, access controls, and attack vector containment.
- Applied cybersecurity frameworks and MITRE ATT&CK mapping to analyze live triage exercises in simulated enterprise environments.
Education
Academic foundations in Computer Science, Networking, and Information Technology.
Fazaia Inter College, Shaheen Camp
Intermediate in Computer Science (ICS)
Peshawar, Pakistan
June 2024 – June 2026Key Highlights
- Computer Science, Physics, and Advanced Mathematics foundation
- Algorithmic thinking and software fundamentals
- Completed Intermediate certification in the ICS track
Fazaia Inter College, Shaheen Camp
Matriculation in Science
Peshawar, Pakistan
May 2022 – May 2024Key Highlights
- Comprehensive foundation across Science, Physics, and Mathematics
- Developed analytical aptitude for computer science disciplines
Featured Projects
Real-world simulations, packet dissection, SIEM dashboards, and incident triage.
Network Traffic Analyzer
Captured and dissected network traffic using Wireshark in a controlled lab to inspect anomalous communication flows during simulated malware infections.
Outcomes
- Identified compromised hosts via NBNS, Kerberos, and SAMR activity.
- Extracted malicious payloads and decoded encrypted TLS handshakes.
Home SIEM Detection Lab
Engineered a virtualized enterprise SIEM lab deploying Splunk Enterprise and Wazuh agents to ingest, normalize, and monitor endpoint security logs.
Outcomes
- Centralized Windows Event Logs (Security, System, Sysmon).
- Built custom alerts detecting brute force and credential dumping.
Active Directory Enterprise Lab
Configured a full Windows Server AD DS environment to evaluate domain privileges, group policies, and identity access control vectors.
Outcomes
- Managed OUs, user hierarchies, and privilege delegations.
- Enforced hardening GPOs and password compliance baselines.
Windows Event Log Analysis
Simulated attacker behavior and credential hunting techniques, analyzing generated Windows Event IDs (4624, 4625, 4672, 7045) in Event Viewer.
Outcomes
- Mapped anomalous execution traces to MITRE ATT&CK tactics.
- Differentiated between false positives and malicious intrusions.
Phishing Email Forensics
Dissected malicious and spoofed email headers to identify sender impersonation, malicious redirects, and forged SPF/DKIM/DMARC records.
Outcomes
- Evaluated Return-Path, DKIM signatures, and header hops.
- Extracted weaponized links and isolated sandbox attachments.
Incident Response Case Study
Walked through full lifecycle triage of an enterprise ransomware intrusion following the NIST SP 800-61 incident response framework.
Outcomes
- Structured artifact collection across identification and containment.
- Formulated actionable indicators of compromise (IOCs) and playbooks.
Skills & Capabilities
Practical competencies assessed through simulated labs, CTFs, and real-world tools.
Cybersecurity & SOC
Security & SIEM Tools
Networking & Infrastructure
Certifications
Click any certificate to expand full high-resolution verification.
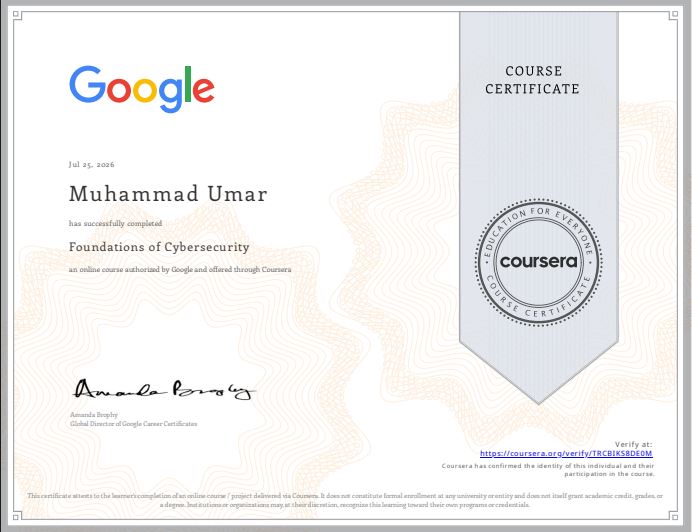
Google Cybersecurity Professional Certificate
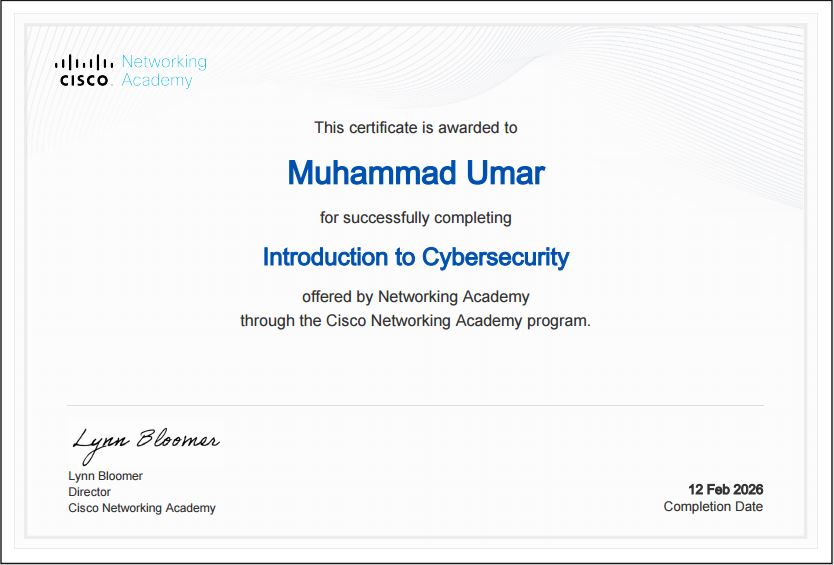
Introduction to Cybersecurity
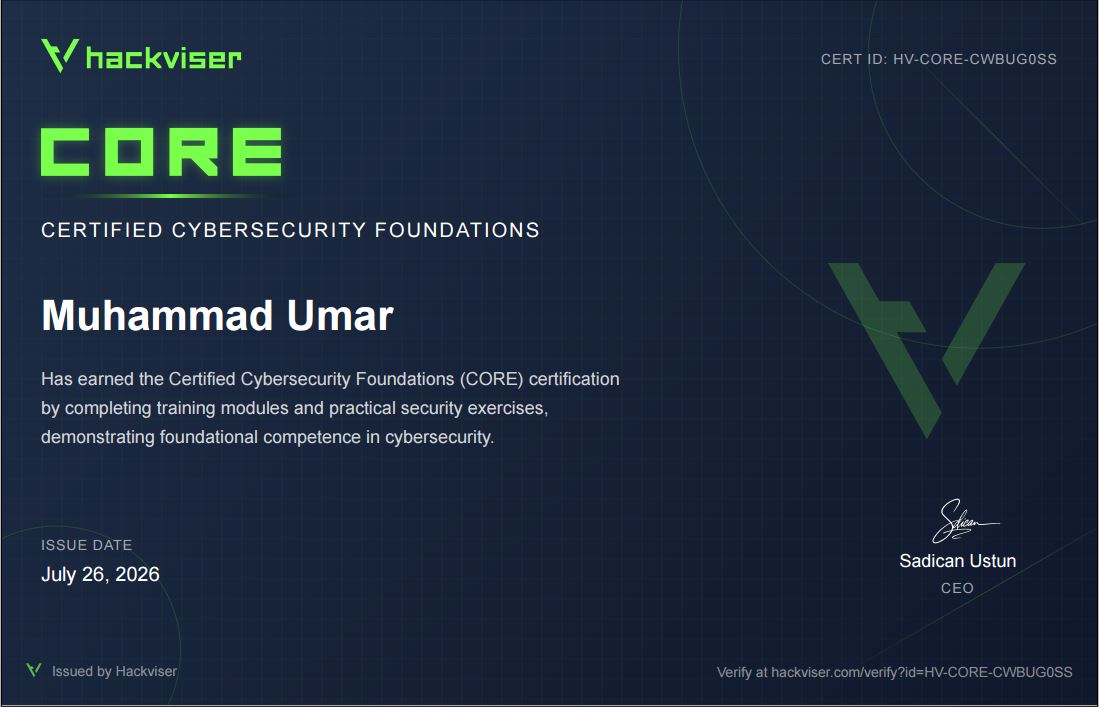
Certified Cybersecurity Foundations
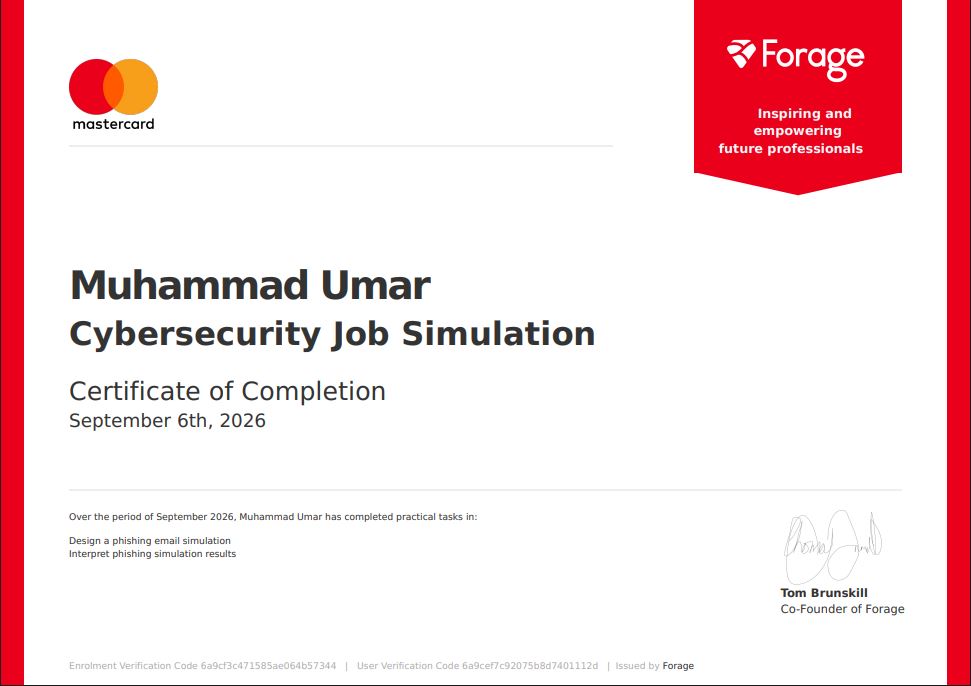
Cybersecurity Job Simulation
Key Metrics & Achievements
Consistent hands-on engagement and technical milestones.
Cybersecurity Internship
Building and evaluating python security scripts and practical defensive modules on an ongoing monthly project roadmap.
Summer of Cybersecurity 2026
Immersive interactive sessions, network forensics workshops, and blue team adversary containment mentorship.
Industry Certification Track
Attained foundational security credentials validating network architecture defense, packet inspection, and operational SIEM triage.